nginx2root: Five nginx RCEs, a Kernel Chain to Root, and the Triage That Tells You Which Hit You
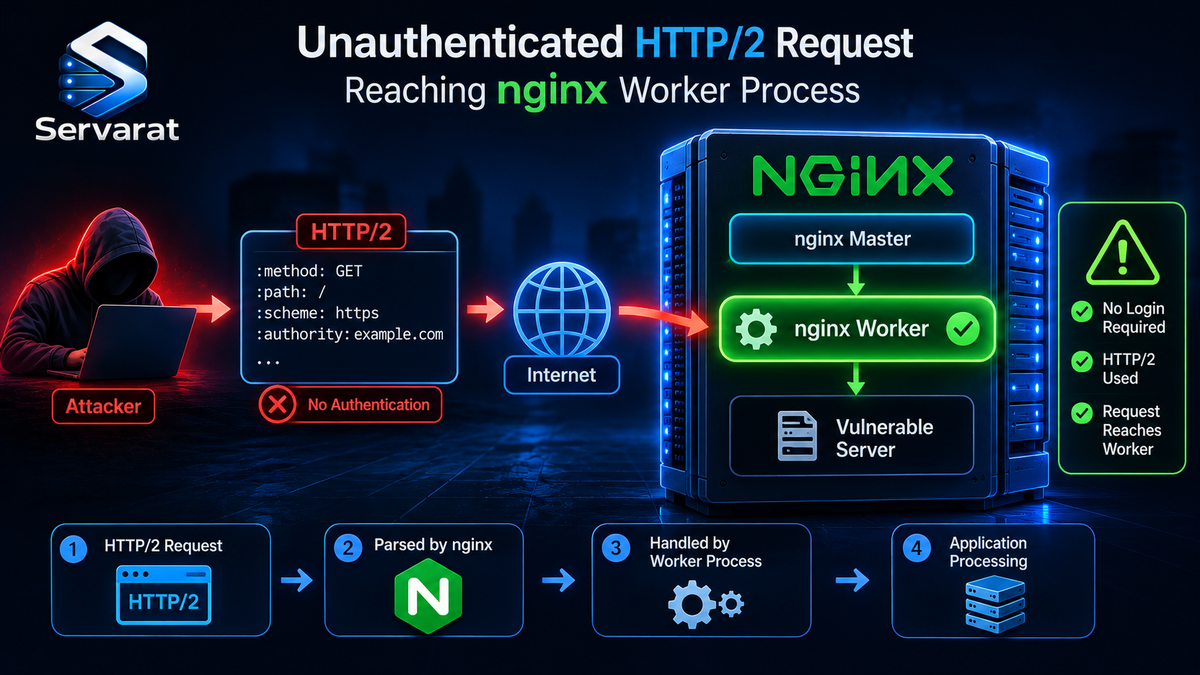
An unauthenticated remote code execution bug in nginx has been the holy grail of web-server research for a decade, and the Xint team just disclosed five at once, plus a kernel bug that chains any of them to root on the host (and out of a Docker container). They call the set nginx2root. If you run nginx anywhere, this is a patch-tonight event, and the headline bug (CVE-2026-123007) has been sitting in every HTTP/2-capable release since 2015. This is the defender's writeup: what each flaw needs to be exploitable, how to check your own exposure in a few commands, what to do before and after the patch lands, and the detection signals that matter. I am deliberately not covering how the exploits work beyond the level needed to understand why a mitigation closes a path.
What nginx2root Actually Is
Six vulnerabilities: five independent RCEs in nginx and one Linux kernel privilege escalation that chains to any of them.
| CVE | Affected configuration | First affected release | Disabling HTTP/2 blocks it? |
|---|---|---|---|
| CVE-2026-123007 | HTTP/2 enabled (the big one) | 1.9.5 | Yes |
| CVE-2026-123633 | HTTP/2 forwarding to an upstream backend | 1.19.7 | Yes |
| CVE-2026-123634 | resolver + request-derived proxy_pass + mirror |
1.13.4 | No |
| CVE-2026-121810 | HTTP/3 (QUIC) forwarding to an upstream | 1.25.0 | No |
| CVE-2026-113425 | Mail proxy with proxy on + auth_http |
0.5.15 | No |
Each is an independent path to code execution as the nginx worker process, not root on its own. The root causes, at CVE-description level: 123007 is an integer overflow in HTTP/2 flow-control accounting that leads to an out-of-bounds heap write; the other four are use-after-free bugs (in the DNS resolver, in HTTP/2 and HTTP/3 connection reuse under load, and in the mail proxy's auth path). Worker-level code execution is already serious, it means reading and writing anything the worker can, dropping a webshell, pivoting, but the kernel half is what turns it into a full host takeover (Section on the SCTP chain below).
⚠️ CVE-2026-123007 is the one that matters for almost everyone. It only needs HTTP/2 to be enabled, which is the default on essentially every modern HTTPS site. It has been present since nginx introduced HTTP/2 in 1.9.5 (2015) and is in every release through 1.31.8, including the development branch as of November 10. Xint's Shodan sweep found that of internet-facing nginx hosts reporting an identifiable version, 98.9% fell in the affected 1.9.5-to-1.31.8 range. A recent version does not save you here.
The Fix, With the Detail the First Advisories Missed
⚠️ There are two fixed releases, and which one you need depends on your branch:
- Stable branch: nginx 1.30.7
- Mainline branch: nginx 1.31.9
A lot of early coverage said only "update to 1.31.9," which sends stable-branch users (common in production and in distro packages) chasing a mainline version they are not on. Check which branch you run and update to the matching fix, both carry the full set of fixes.
⚠️ And the distro-backport trap, same as every nginx CVE: the version string from nginx -v does not change when a distribution backports a security fix. Ubuntu 24.04 ships 1.24.0, Ubuntu 22.04 ships 1.18.0, Debian 12 ships 1.22.1, and each may patch the vulnerable code while still reporting the old number. Compare the full package version against your distro's security advisory, not the nginx version string.
Check Your Own Exposure
For the HTTP/2 bug (CVE-2026-123007), a host is exposed only if all of these are true: unpatched version, HTTP/2 module compiled in, HTTP/2 enabled in config, and (for internet risk) HTTP/2 reachable from outside. Four quick checks.
1. Version:
nginx -v 2>&1
1.9.5 through 1.31.8 means the official release contains the vulnerable code (continue checking). 1.9.4 or earlier predates HTTP/2 and is not affected. A distro/appliance version string needs the backport check above.
2. Is the HTTP/2 module even built in:
nginx -V 2>&1 | grep -q -- '--with-http_v2_module' && echo 'HTTP2_MODULE=present' || echo 'HTTP2_MODULE=absent'
Absent means this binary cannot be hit by the HTTP/2 bug at all.
3. Is HTTP/2 actually enabled in your config:
sudo nginx -T 2>&1 | sed 's/#.*//' | grep -nE 'listen[[:space:]].*http2|^[[:space:]]*http2[[:space:]]+on[[:space:]]*;'
Any listen 443 ssl http2; or http2 on; line means it is on. (nginx -T reads the on-disk config; if you edited without reloading, the running config may differ.)
4. Is HTTP/2 reachable from the internet (run from outside your network, replace both {HOST}):
openssl s_client -connect {HOST}:443 -servername {HOST} -alpn h2 </dev/null 2>&1 | grep -E 'ALPN protocol:|No ALPN negotiated|handshake failure'
ALPN protocol: h2 means the server accepts HTTP/2 from the internet. ⚠️ If a CDN or reverse proxy fronts nginx, this test only reaches the proxy, so also run it directly against the nginx host.
Across a fleet, the combined version-plus-module check in one loop:
for h in $(cat hosts.txt); do v=$(ssh -o ConnectTimeout=5 "$h" 'nginx -v 2>&1' 2>/dev/null); m=$(ssh -o ConnectTimeout=5 "$h" "nginx -V 2>&1 | grep -q -- '--with-http_v2_module' && echo present || echo absent" 2>/dev/null); printf '%s: %s | http2_module=%s\n' "$h" "${v#nginx version: }" "${m:-unreachable}"; done
Before the Patch: Mitigations by Configuration
Disabling HTTP/2 blocks the two biggest paths (123007 and 123633) but not the other three. Apply the ones matching your setup.
Disable HTTP/2 (blocks CVE-2026-123007 and CVE-2026-123633). For nginx 1.25.1+, in each affected server block:
listen 443 ssl;
http2 off;
For 1.9.5 through 1.25.0, remove http2 from the listen line (listen 443 ssl http2; becomes listen 443 ssl;). ⚠️ Services that require HTTP/2, native gRPC in particular, break when you do this; HTTP/1.1 clients are unaffected. Validate and reload, then re-run exposure check 4 to confirm h2 is gone.
Disable HTTP/3 / QUIC (CVE-2026-121810), if you run it. Remove the quic listen directives, set http3 off;, and clear the Alt-Svc advertisement:
listen 443 ssl;
http3 off;
add_header Alt-Svc 'clear' always;
Then confirm nothing still answers UDP on 443:
sudo ss -lunp 'sport = :443'
If nginx still shows there, block UDP/443 at the firewall as backup.
Remove request-time DNS lookups (CVE-2026-123634), if you use a variable in proxy_pass (like proxy_pass http://$host;) together with mirror. Point proxy_pass at a fixed upstream group instead so there is no per-request DNS resolution. ⚠️ Setting mirror_request_body on alone does not fix the underlying bug; do not rely on it. And other subrequest features (SSI, for example) can reach the same bug, so turning off mirror alone does not fully cover it, a fixed upstream is the reliable mitigation.
Restrict the mail proxy (CVE-2026-113425), if you front IMAP/POP3/SMTP with nginx using proxy on + auth_http. Bind the mail listeners to loopback if external access is not needed, or firewall them to trusted IPs. The attacker does not need valid credentials for this one.
⚠️ Reloading is not enough, and this catches people. A config reload applies only to new connections; existing HTTP/2 and mail sessions stay on the old workers with the old config. More importantly, after you install the actual patch, a reload does not replace the running executable, you must systemctl restart nginx (a brief interruption) or do a supported live binary upgrade. A reloaded-but-not-restarted nginx is still running the vulnerable binary.
Detection: What a Hit Looks Like
⚠️ The HTTP/2 attack leaves little in access logs, the control frames it abuses (WINDOW_UPDATE, RST_STREAM) are not logged as requests and are TLS-encrypted in transit. So the strongest signal is behavioral, not log-based.
The clearest sign: an nginx worker running a program. A worker has no legitimate reason to exec a shell or any external binary. If you run auditd, add a rule on the worker's UID (find it with ps -eo uid,user,args | grep '[n]ginx: worker'):
sudo auditctl -a always,exit -F arch=b64 -S execve,execveat -F euid=NGINX_UID -k nginx_worker_exec
Then review with sudo ausearch -k nginx_worker_exec -ts recent -i and look for /bin/sh, /bin/bash, or anything else spawned by a worker. ⚠️ The rule only records executions after it is installed, so an empty result does not rule out an earlier compromise. This is the same execve-watch discipline from catching a Linux compromise with auditd, pointed at the web-server worker specifically.
Weaker signals, suspicious only in combination: a single external IP holding a connection open for minutes with bytes_received climbing fast while the server sends little back (check with sudo ss -tinp state established '( sport = :443 )' run twice a few seconds apart), the same IP also opening many short-lived TLS connections, and repeated abnormal worker exits or segfaults in the error log (grep -Ei 'worker process.*exited|signal 11|segfault' /var/log/nginx/error.log). A failed exploit attempt can crash a worker, and attackers retry, so a burst of worker crashes from one source is worth investigating. None of these alone proves anything; a worker running a shell does.
If you confirm a worker executed something it should not have, treat the host as compromised and work it forensically, preserve first, find the entry point, hunt persistence beyond the obvious, the order laid out in why Linux servers get compromised.
The Kernel Half: Worker-to-Root and Container Escape
The nginx bugs give an attacker the worker's limited privileges. Xint chained them to a Linux kernel use-after-free in the SCTP subsystem to reach root on the host, and crucially, that worked even with nginx running inside a Docker container, root on the container's worker became root on the underlying host, and therefore every container on it, because containers share the host kernel.
⚠️ This is the second serious SCTP kernel UAF disclosed in recent months (the other was SCTPhantom), and the defense is identical and worth applying fleet-wide regardless of nginx: if a host does not need SCTP, block the module so this and future SCTP kernel bugs cannot be reached.
echo 'install sctp /bin/false' | sudo tee /etc/modprobe.d/disable-sctp.conf
⚠️ This prevents on-demand loading only; it does not unload SCTP if already loaded, and does not help if SCTP is compiled into the kernel. On a host where lsmod | grep sctp shows it loaded, unload it (sudo modprobe -r sctp, fails if in use) or reboot after adding the block. For a normal web/app server, blocking SCTP is safe and removes a whole class of kernel-escalation surface. Xint is withholding the SCTP exploit details until a kernel patch ships, so the module block is the mitigation to apply now. For container hosts specifically, this plus dropping unneeded capabilities is the real containment, since the shared kernel means a kernel UAF is a container-escape primitive no matter how clean your container config is.
The Pattern Worth Noting
⚠️ One Xint researcher found the HTTP/2 bug by hand; a fully automated scan found the other four without human guidance. nginx recorded two advisories in all of 2025 and 26 by mid-November 2026. This is the collapsing patch-to-exploit window applied to the most-audited web server on the internet: AI-assisted research is surfacing memory-corruption bugs in decades-old, heavily-reviewed code faster than ever, and CVE-2026-123007 survived ten years of that review until an automated tool went looking. The operational consequence is not panic, it is that your patch cadence for internet-facing infrastructure has to assume this discovery rate, which means fast, verified patching and a standing exposure inventory rather than a quarterly sweep.
Bottom Line
nginx2root is a genuine patch-tonight event, and CVE-2026-123007 (HTTP/2) reaches almost every nginx on the internet. Run the four exposure checks, prioritize internet-facing hosts with HTTP/2 enabled, and update to 1.30.7 on the stable branch or 1.31.9 on mainline (not just 1.31.9, check your branch), confirming the backport if you run distro packages. Until the patch is on, disable HTTP/2 where you can live without it, apply the config-specific mitigations for HTTP/3, resolver+mirror, and the mail proxy, and remember that a reload does not swap the running binary, restart nginx after patching. Watch for the one signal that actually means compromise, an nginx worker running a program, and block the SCTP kernel module on hosts that do not need it to deny the chain to root. The bug hid for a decade; the fix is a version bump and a restart, so there is no reason to be the server still running 1.31.8 next week.
References
- Xint: NGINX2Root, New Remote Code Execution Vulnerabilities in nginx Require Urgent Patching (source)
- nginx security advisories
- nginx 1.30.7 and 1.31.9 release notes
- Equixly: nginx2root, Disabling HTTP/2 Stops Two of Five nginx RCE Flaws
- SecurityOnline: NGINX2Root (CVE-2026-123007) NGINX RCE Explained
- nginx2root.com